Hippo Digital, the Leeds-based digital consultancy that builds and runs services for the UK public sector, has joined the Software Security Ambassadors Scheme run by the Department for Digital, Culture, Media and Sport (DCMS) and the National Cyber Security Centre (NCSC). Hippo announced it on November 3, 2026, the day GOV.UK updated the scheme’s second group of signatories to include it. If you buy software or development work in the UK, the more useful part of the news is the code the scheme promotes, because it gives you a clear set of questions to put to any supplier.
What the scheme is
The scheme is a group of firms that have agreed to champion the government’s Software Security Code of Practice and show how they apply it. It is not a certification. GOV.UK says plainly that the scheme “is not an assessment scheme” and that buyers should not use membership as a criterion in procurement or tendering. It points buyers to the code’s self-assessment instead.
The code itself is voluntary. DCMS and the Department for Science, Innovation and Technology published it in May 2025, built with NCSC experts and industry and academic advisers, and it is co-sealed by the Canadian Centre for Cyber Security. It sets out 14 principles that software vendors are expected to meet, aimed at cutting software supply chain attacks and other avoidable failures in how software is built and maintained.
What Hippo has committed to
Hippo has committed to four things over the next 12 months, according to its announcement:
- naming a Senior Responsible Owner who is formally accountable for implementing the code
- completing and publishing its self-assessment against the code’s principles
- training its delivery teams in secure software development
- sharing case studies and lessons from putting the code in place with government and industry
Those line up with what GOV.UK asks of every software supplier that signs up, which also includes helping test a pilot third-party assessment of the code and encouraging clients to adopt its principles when software is built together. Darren Hutton, Hippo’s Chief Digital Officer, said the code “provides clear and practical standards for vendors, resellers and buyers to ensure their software design and procurement have security built in.”
What the code asks of a software supplier
The code groups its principles into four areas, which Hippo summarizes in its announcement:
- secure design and development: an established secure development framework, knowing the third-party components in your software and testing before release
- build environment security: protecting the build environment from unauthorized access, and controlling and logging changes to it
- secure deployment and maintenance: distributing software securely, publishing a vulnerability disclosure process and shipping timely security updates
- communication with customers: being open about the support and maintenance you can expect, the product lifecycle and notable incidents
Why it matters if you are hiring a development firm
It gives you a checklist that does not depend on taking a firm’s word for it. Whichever custom software development company you talk to, you can ask whether it has completed the code’s self-assessment and whether you can see it, who is accountable for software security, how it tracks the open source and third-party components in what it builds, and what its vulnerability disclosure and patching process looks like. A firm that has done the self-assessment should be able to answer all of those quickly.
The self-assessment is the part to ask for, not the ambassador badge. Hippo will publish its own within the year, so it is worth checking back on its site. If security is the main concern on your project, you can also compare cybersecurity consulting firms and IT consulting firms on TechBonna.
Who else is in the scheme
Hippo sits in the second group of signatories alongside DCMS, the NCSC, Capgemini, Fortinet, QinetiQ, Thales, Zscaler, the SANS Institute and others. The first group includes Accenture, Cisco, NCC Group, Palo Alto Networks, Sage, Santander and Lloyds Banking Group.
Where this fits in Hippo’s year
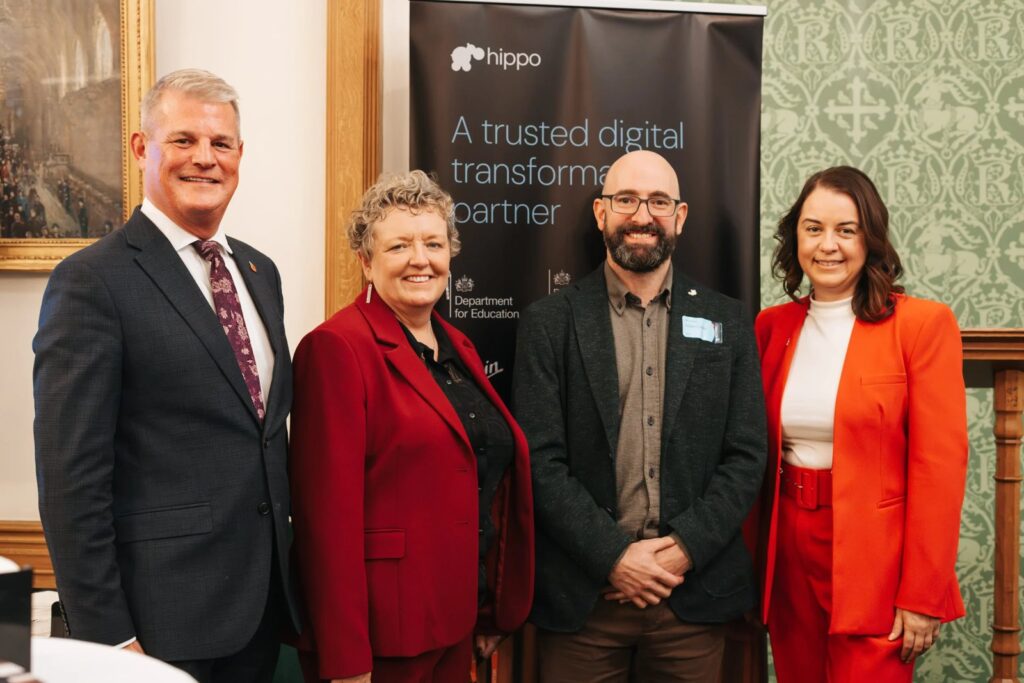
The announcement came the same day Hippo marked ten years in business with a reception at the Houses of Parliament, where it launched a policy paper on how government delivers digital change. The firm is headquartered in Leeds with a UK-based workforce and works across health, justice, education and financial services. In October it joined Anthropic’s Claude Partner Network as a Certified Services Partner, and in June it was appointed to the government’s RM6200 Artificial Intelligence procurement framework.
This story is based on desk research of Hippo’s announcement of November 3, 2026 and the scheme and code pages on GOV.UK.
Sources: Hippo, November 3, 2026; GOV.UK, Software Security Ambassadors group 2 signatories; GOV.UK, Software Security Code of Practice.